High Availability Palo Alto (Active/Standby)

 High Availability is usually performed in most of the data centers networks today which ensures application availability . High Availability is usually achieved in case one of the appliance goes down or have some physical or logical connectivity issues. 

Achieving high availability in Palo Alto firewall is relatively very easy. Palo Alto firewall can work in both Active/Standby mode or in Active/Active. We will basically be talking about Active/Standby mode in this article. There are basically two links that needs to be configure in Palo Alto for HA.

1. Control Links

Control Links are associated with control plane traffic which is mainly used for heartbeat exchanged, configuration synchronization. Dedicate HA ports are available in higher series of Palo Alto or even a HA interface can be created for some inband ports.  

2. Data Links

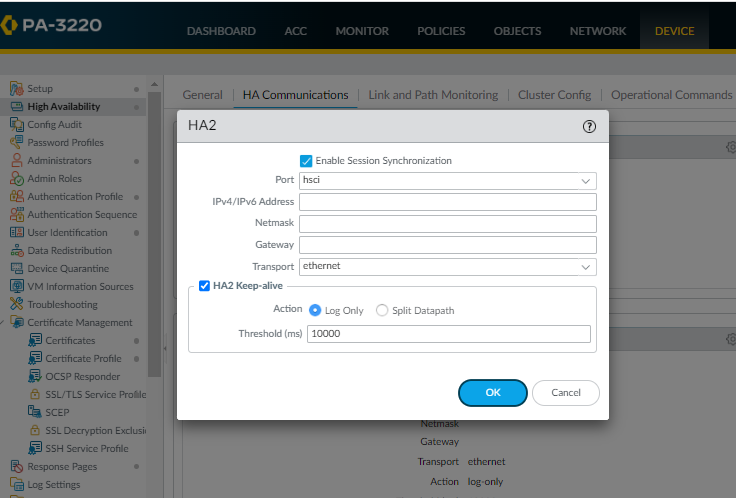
Data Links are mainly used for session synchronization, forwarding table synchronization. Dedicated HSCI Ports are available for higher end Palo Alto  whereas as mentioned earlier inband ports can also be used. 


3. Backup Link

Backup Link can be configured for both Control Link (HA1) and Data Link (HA2). Backup Links is also important incase of primary link going down.

1. Configuration
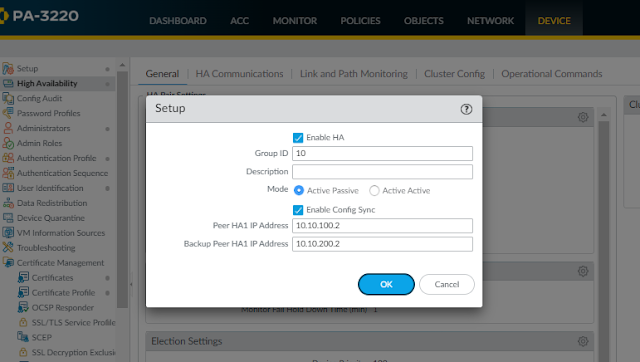
  • Control Link  needs to be configured with a point to point IP and Data Link can be configured with IP, ethernet or UDP as a transport connection.
  • Group ID also needs to be mentioned with group id being same on both the boxes.
  • Mode will be Active/Passive.
  • Device Priority with lesser number will be in active state.
  • Preemption must be enabled only on the primary device.
  • Inband data ports can also be as High Availability ports for control link , data link as well as for backup links
1.1 SETUP 
1.1.1 PA- PRIMARY 


1.1.2 PA-SECONDARY


1.1.3Control Links - PA Primary

1.1.4 Control Links - PA Secondary

1.1.5 Data Links - PA Primary

1.1.6 Data Links - PA Secondary


Configuring High Availability in Palo Alto  is relatively very easy. Main thing is grabbing the basic theoretical concept of how HA works. There are also things like Link and Path Monitoring in High Availability which is quite awesome and will talk about it in some other blog. Let me conclude my blog here as it is getting quite lengthy.


Comments

Popular posts from this blog

SAN Switch Zoning with Brocade

Zoning in Brocade SAN Switch Let's begin with resetting the switch completely. In my environment I have two brocade SAN Switch connecting to 2 Dell R940 server configured with VMware. The SAN switch will be having connectivity between Dell Unity 500 storage and Dell R940 servers. Multipathing will be done between the server and storage with the help of SAN Switch. Multipathing, also called SAN multipathing or I/O multipathing, is the establishment of multiple physical routes between a server and the storage device that supports. It results in better fault tolerance and performance enhancement. DESIGN The idea behind zoning is that intended WWPN talk with each other . This is more like ACL in the world of Ethernet. To see the devices which are logged into the switch the following commands can be executed. SAN-A:admin> switchshow switchName: SAN-A switchType: 118.1 switchState: Online switchMode: Native switchRole: Principal switchDomain: 1 switchId: ...

POLICY ROUTES FORTIGATE

 Policy routes also referred to as policy based routing is a very popular technique that routes the incoming packets based on the set of policy defined. The policy usually defines that the packet from particular source are routed to particular gateway.  Simply not trying to make it theoretically lengthy lets try this feature out in Fortigate. In our particular scenario there are 2 fortigate boxes residing in HA (Active/Passive) mode. There are two upstream ISP connected with the fortigate box one named after port 1 SUBISU and the other being port 2  WEBSURFER. We have two internal gateways which contains subnet of 172.16.0.0/28 and the other one being 172.16.0.16/28. We will be leveraging the privilege of policy route and send the packet incoming from 172.16.0.0/28 subnet towards Websurfer upstream and the packet coming from 172.16.0.16/28 subnet towards SUBISU upstream which will help us on utilizing both the links making it more efficient usage of bandwidth. We will nee...